Our Methodology
Human-Led, AI-Assisted Penetration Testing
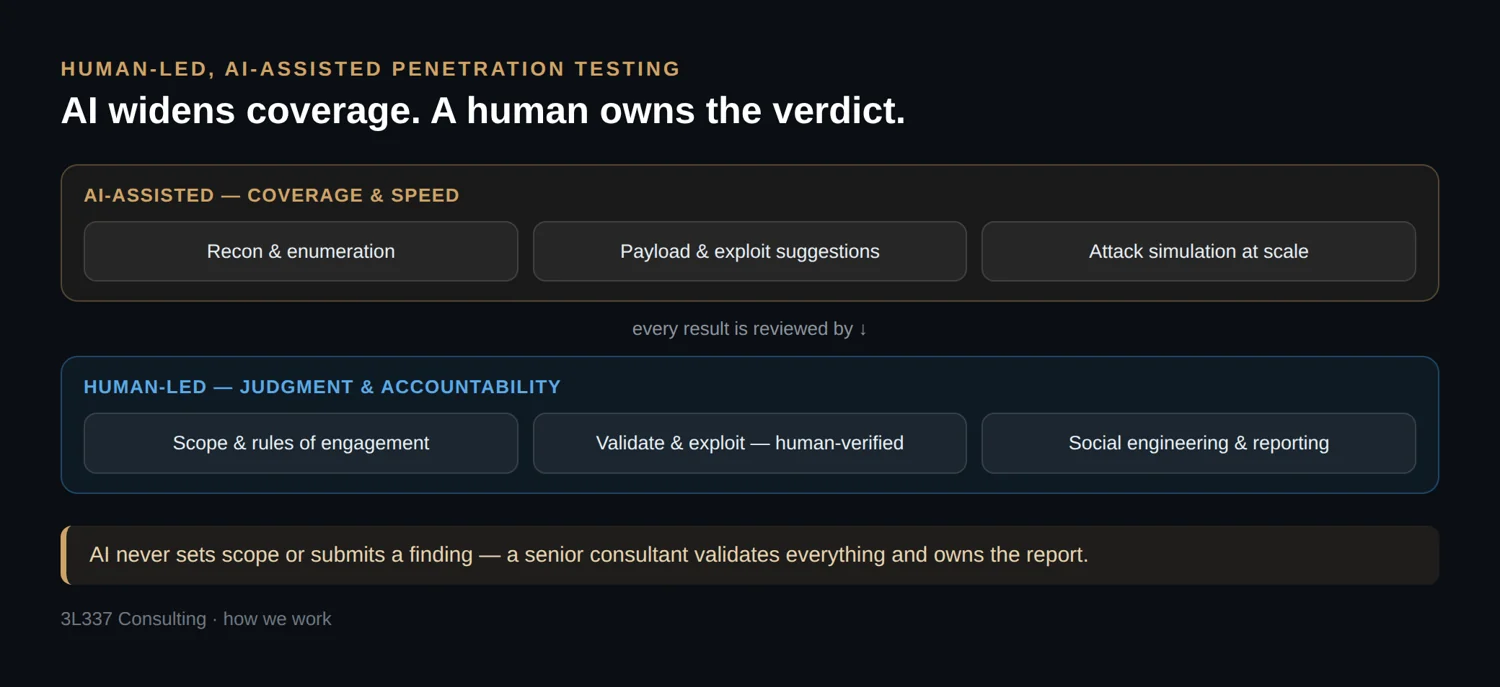
AI improves coverage, consistency, and speed. Senior consultants still define the test, validate every finding, and own the report.
At 3L337, senior consultants define the test strategy, validate every finding, assess business impact, and own the final report. Automation and AI widen coverage and accelerate the routine — never the judgment.
What “human-led, AI-assisted” means
Human-led scoping
A senior consultant defines what is in scope, what is off-limits, and how we test — before any testing begins.
AI-assisted coverage
Automation and AI help enumerate the attack surface, generate attack-path hypotheses, vary payloads, normalize evidence, and support reporting.
Human validation
Every issue is reproduced and confirmed by a consultant. If a person hasn’t verified it, it does not go in your report.
What AI does not do
- Replace analyst judgment
- Decide scope
- Autonomously attack your environment
- Invent or submit unverified findings
- Guarantee exhaustive coverage
How we handle your data. 3L337 works to keep client data out of third-party and frontier AI systems. Where frontier models are used to improve results, if you ask us not to use frontier models with your data, we will not. Data handling is agreed as part of scoping, in writing.
Our process
Scope & rules
Targets, constraints, testing windows, authorization, and data handling agreed up front.
Recon & hypotheses
AI-assisted enumeration and attack-path hypotheses across the defined scope.
Dynamic validation
Hands-on exploitation and safe proof — real attack paths confirmed by a consultant, not scanner output.
Triage & business context
Each finding is assessed for exploitability and what it actually means to your business.
Report QA & remediation
Senior review of every finding, clear evidence, prioritized fixes, and support as you remediate.
What you receive
- An executive summary your leadership can act on
- Reproducible evidence for every finding
- Business-impact and severity rationale, not just a CVSS number
- Prioritized, engineering-ready remediation guidance
- Remediation support or a retest, when included in scope
Why 3L337. Senior offensive-security consultants with deep, hands-on delivery experience — including a SANS Senior Instructor and SEC542 co-author, roughly 30 years in IT and information security (about 17 of them dedicated to security), and certifications including OSCP, GXPN, GPEN, GWAPT, GAWN, GWEB, and GPYC. Clear, evidence-driven reporting is the product.
Ready to scope an engagement?
Tell us what you need to validate and we’ll recommend the right engagement.